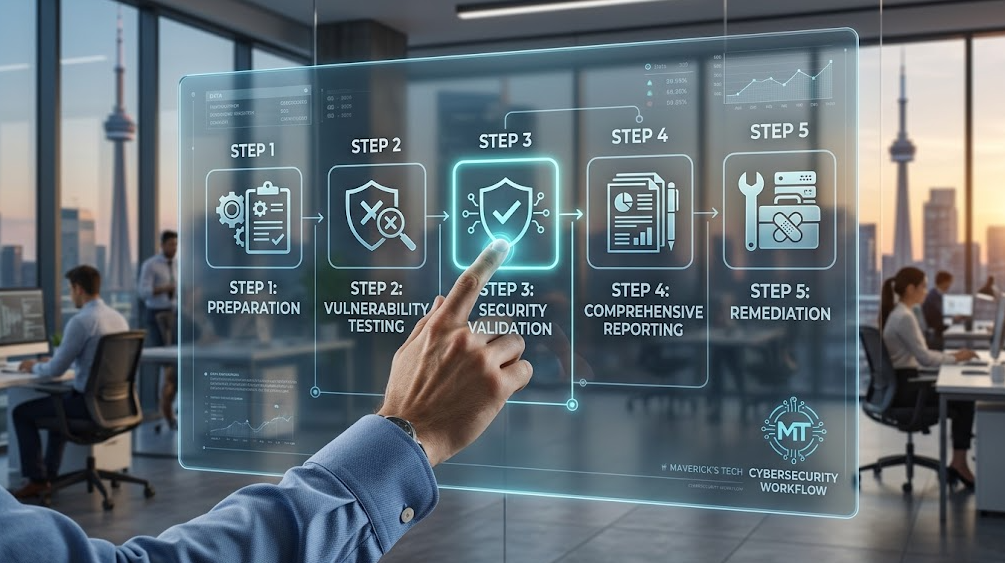
A professional penetration test is more than running automated security tools against a website or network. Effective testing follows a defined process that begins with understanding the environment and ends with clear remediation guidance. For organizations planning a security assessment, understanding this process helps set realistic expectations and ensures that the final results are useful to both technical teams and business decision-makers.
Professional penetration testing services Toronto can involve several stages, including planning, reconnaissance, controlled exploitation, vulnerability validation, reporting, and remediation support. The exact methodology depends on the scope, technology, objectives, and risk profile of the organization being tested.
1. Defining the Scope Before Testing Begins
The quality of a penetration test depends heavily on how clearly the engagement is defined.
Before any technical testing takes place, the organization and testing team need to establish what is authorized for assessment. This may include specific domains, applications, APIs, IP addresses, cloud resources, network segments, or other infrastructure.
A well-defined scope should address questions such as:
- Which systems are included?
- Which systems are excluded?
- What testing techniques are permitted?
- Are production systems part of the assessment?
- What testing window will be used?
- Who should be contacted if an unexpected issue occurs?
- How will potentially sensitive information discovered during testing be handled?
This planning stage reduces ambiguity and helps prevent accidental testing of systems that are outside the engagement.
External, Internal, and Application Testing
The scope can take different forms.
An external assessment examines assets that are reachable from outside the organization’s environment. Internal testing evaluates what an attacker or compromised employee account might accomplish after gaining internal access. Application testing focuses more closely on software functionality, authentication, authorization, data handling, and application logic.
Some engagements combine several approaches when the organization needs a broader view.
2. Gathering Information About the Target
Once the scope is established, testers collect information that can help them understand the environment.
This reconnaissance phase may involve identifying publicly exposed services, application technologies, domains, subdomains, accessible interfaces, and other relevant information within the authorized scope.
The objective is not simply to collect as much information as possible. It is to build an accurate picture of the attack surface.
For example, a company may know that it operates one public website, while testing reveals several associated services and application endpoints that are also publicly accessible.
Understanding the complete attack surface provides a better foundation for subsequent testing.
3. Mapping Potential Attack Paths
After initial reconnaissance, testers examine how the discovered components interact.
A web application might communicate with several APIs. Those APIs may connect to databases or third-party services. Authentication may be handled by a separate identity platform.
Security weaknesses can emerge at the boundaries between these components.
Testers therefore consider questions such as:
- Does authentication work consistently across interfaces?
- Are authorization controls enforced at every relevant endpoint?
- Can users access resources belonging to other accounts?
- Are sensitive functions protected against unauthorized requests?
- Does the application expose information that could assist an attacker?
- Can one compromised component provide access to another?
This stage turns a collection of technical assets into a model of how the environment could potentially be attacked.
4. Testing for Security Weaknesses
The next stage involves actively testing the systems within the agreed scope.
Depending on the engagement, testers may examine authentication, authorization, session management, input validation, configuration, exposed services, access controls, and other security mechanisms.
Automated tools can assist with discovery and repetitive checks, but professional testing often requires manual analysis as well.
Why Manual Validation Matters
Automated results can contain false positives, incomplete findings, or insufficient context.
Suppose a scanner identifies a potentially vulnerable component. That result does not necessarily demonstrate that the weakness can be exploited in the organization’s specific environment.
Manual validation helps determine whether the issue is real and what its practical consequences may be.
This is particularly relevant for application logic vulnerabilities, authorization problems, business-process flaws, and attack chains that require several steps.
5. Controlled Vulnerability Validation
Finding a suspected weakness is not always the same as proving its significance.
During controlled validation, testers determine whether an identified issue can produce the expected security impact without unnecessarily disrupting the target environment.
The approach should remain proportionate to the agreed rules of engagement.
For example, if a weakness appears capable of exposing unauthorized information, testing may seek to demonstrate the issue using limited, appropriate evidence rather than accessing unrelated sensitive records.
The purpose is to establish credibility and impact while maintaining responsible testing practices.
6. Prioritizing Findings by Risk
A penetration test can uncover multiple findings, but not every finding deserves the same level of urgency.
Effective reporting considers factors such as:
- Likelihood of exploitation
- Required attacker access
- Complexity of exploitation
- Sensitivity of affected information
- Potential operational consequences
- Exposure of the affected system
- Whether multiple weaknesses can be combined
A lower-severity issue may become more important if it forms part of an attack chain leading toward a sensitive system.
Conversely, a technically serious issue may have limited practical impact if strong compensating controls prevent exploitation.
Risk-based interpretation makes the results more useful than a simple list of scanner output.
7. Building a Clear Penetration Testing Report
The final report should allow different audiences to understand the results.
Technical teams generally need detailed information that helps them reproduce and remediate findings. Executives and managers may need a concise explanation of overall exposure, business implications, and priority areas.
A useful report can include:
Executive Summary
This section explains the overall security picture in accessible language and highlights the most significant findings.
Technical Findings
Each finding should provide sufficient evidence and explanation to help the responsible team understand the problem.
Risk Rating
The report should communicate the relative importance of each issue and explain the reasoning behind the priority.
Remediation Guidance
A useful assessment does not stop at identifying the problem. It should provide practical direction for reducing the associated risk.
Supporting Evidence
Where appropriate, screenshots, request examples, response information, or other controlled evidence can help demonstrate what was observed during testing.
8. Turning Findings Into Remediation Work
A penetration test only creates lasting value when its findings lead to action.
After receiving the report, organizations can categorize findings according to urgency and assign them to appropriate owners.
For example, an application authorization flaw may require developer involvement, while an exposed service or network configuration issue may belong to an infrastructure team.
The remediation process should also consider the root cause.
If several applications contain similar authorization weaknesses, fixing each individual instance may not be enough. The organization may need to improve development standards, code review procedures, security testing, or application architecture.
9. Retesting After Corrections
Remediation should ideally be followed by validation when the nature of the finding warrants it.
A retest determines whether the corrective action successfully addressed the original weakness.
This is especially useful for vulnerabilities involving configuration changes, authentication controls, access restrictions, or application code.
The goal is not merely to confirm that a particular test case no longer works. The organization should also consider whether the underlying weakness has actually been eliminated rather than simply hidden by a temporary change.
How Organizations Can Get More Value From Testing
Organizations can improve the usefulness of a penetration test by preparing in advance.
Before the engagement, teams should:
- Identify critical applications and systems.
- Define clear testing objectives.
- Confirm authorized targets and exclusions.
- Identify appropriate technical contacts.
- Communicate testing windows to relevant personnel.
- Prepare a process for handling discovered vulnerabilities.
- Allocate resources for remediation after the assessment.
This preparation prevents a common mistake: treating the penetration test as the end of a security project instead of the beginning of a remediation cycle.
Key Takeaway
Professional penetration testing is a structured security process rather than a single scan. The strongest engagements connect planning, reconnaissance, technical testing, vulnerability validation, risk interpretation, reporting, remediation, and—when appropriate—retesting.
Each stage serves a different purpose. Clear scope prevents confusion. Reconnaissance reveals the attack surface. Manual testing provides context. Validation establishes practical impact. Reporting translates observations into actionable findings, while remediation turns those findings into measurable security improvements.
Conclusion
A well-executed penetration test should leave an organization with a clearer understanding of its real security exposure.
The value comes not only from discovering vulnerabilities but from determining which weaknesses matter most, demonstrating their practical significance, and providing enough information for teams to address them effectively.
For organizations evaluating security testing, understanding the complete testing lifecycle makes it easier to select an appropriate assessment, prepare internal teams, interpret the final report, and turn security findings into meaningful improvements.